Blog
Patch Tuesday September 2026 (966 flaws, 105 rated as "Critical, 2 Active Zero Days)
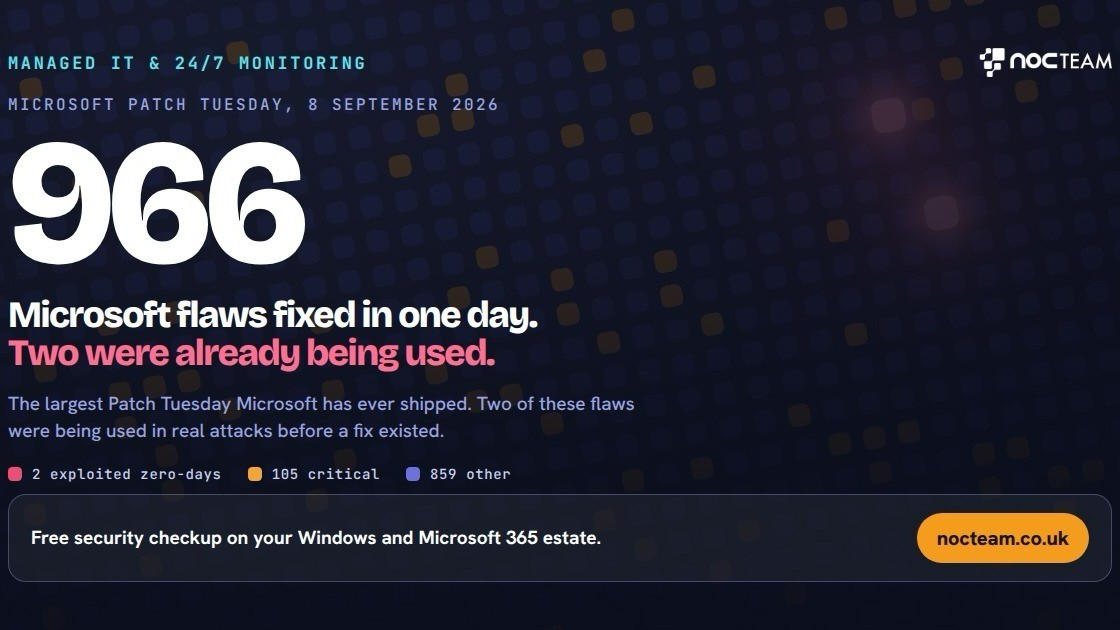
Microsoft has issued security updates for a record-breaking 966 flaws, including 105 vulnerabilities rated as "Critical," as part of the Patch Tuesday updates for September 2026. Following recent massive update cycles, this release marks Microsoft's single largest Patch Tuesday in history,driven primarily by the internal rollout of AI-powered vulnerability discovery tools. The September cycle is anchored by two zero-day vulnerabilities actively exploited in the wild to gain SYSTEM-level access.
Zero-Days Fixed
Microsoft confirmed the inclusion of two actively exploited zero-day flaws this month. Both require local access or sandbox presence, allowing unauthorized actors to elevate privileges straight to SYSTEM:
- CVE-2026-81963 - Windows Update Stack Elevation of Privilege Impact: An improper link resolution ("link following") vulnerability in the Windows Update Stack allowing local authorized attackers to gain SYSTEM privileges.
- CVE-2026-85880 - Windows Advanced Local Procedure Call (ALPC) Elevation of Privilege Impact: A heap-based buffer overflow in the ALPC messaging component that enables attackers running code inside a low-privilege AppContainer sandbox to break isolation and reach full SYSTEM privileges.
Critical Vulnerabilities to Prioritise
Out of the 105 "Critical" flaws, over 80 are Remote Code Execution (RCE) bugs. Core infrastructure services carry multiple unauthenticated CVSS 9.8 vulnerabilities that require immediate mitigation:
- CVE-2026-72982 - Windows Netlogon Service Remote Code Execution (CVSS 9.8)
- CVE-2026-69730 - Windows DNS Server Remote Code Execution (CVSS 9.8)
- CVE-2026-69845 & CVE-2026-72979 - Windows DHCP Server Remote Code Execution (CVSS 9.8)
- CVE-2026-69579 - Windows Message Queuing (MSMQ) Remote Code Execution (CVSS 9.8)
- CVE-2026-55007 - Microsoft Exchange Server Remote Code Execution
Vulnerabilities by Category
The September 2026 updates addressed a total of 966 native Microsoft flaws, categorised as follows:
- Elevation of Privilege Vulnerabilities - 438
- Remote Code Execution Vulnerabilities - 258
- Information Disclosure Vulnerabilities - 173
- Denial of Service Vulnerabilities - 56
- Security Feature Bypass Vulnerabilities - 19
- Spoofing Vulnerabilities - 16
- Total Flaws - 966
Need Help with Patch Management?
Struggling with the relentless pace and record-breaking volume of monthly patching? In 2026, "good enough" security is no longer an option. NOCTeam can secure your environment with proactive Patch Management, M365 hardening, and advanced Endpoint Detection and Response (EDR) services.
Email [email protected] today for a free security checkup of your IT systems.
#PatchTuesday #CyberSecurity2026 #M365 #ZeroDay #VulnerabilityManagement #NOCTeam #Infosec #Remediation #WindowsSecurity #SysAdmin
Originally published on LinkedIn.