For years, the gold standard for enterprise cybersecurity was the Security Operations Center (SOC)—a costly, 24/7 internal team of expert analysts hunting for threats. This model was simply out of reach for most Small and Mid-sized Businesses (SMBs), leaving them reliant on basic antivirus and reactive defence.
Today, that has changed. The rise of Managed Detection and Response (MDR) is democratizing 24/7 threat hunting, offering SMBs a complete, outsourced security team dedicated to rapid defence.
The Problem: Reactive Security is Obsolete
Traditional cybersecurity tools (like firewalls and basic antivirus) are reactive. They only block threats they already recognize. Modern attacks, however, are sophisticated, often exploiting legitimate tools (known as "living off the land") or relying on never-before-seen zero-day exploits.
When an advanced attacker bypasses the initial perimeter, two things happen:
- Dwell Time: The attacker can remain "dormant" inside the network for days or weeks, mapping your data and planning their final move (e.g., ransomware deployment).
- Analyst Overload: If the breach is flagged, internal IT teams—already stretched thin managing infrastructure—must drop everything to become forensic investigators, often lacking the specific expertise or 24/7 coverage required for a swift response.
The Solution: Managed Detection and Response (MDR)
MDR is not just another security tool; it is a service. It combines advanced technology with human expertise to deliver proactive, continuous defence.
1. Advanced Technology: EDR
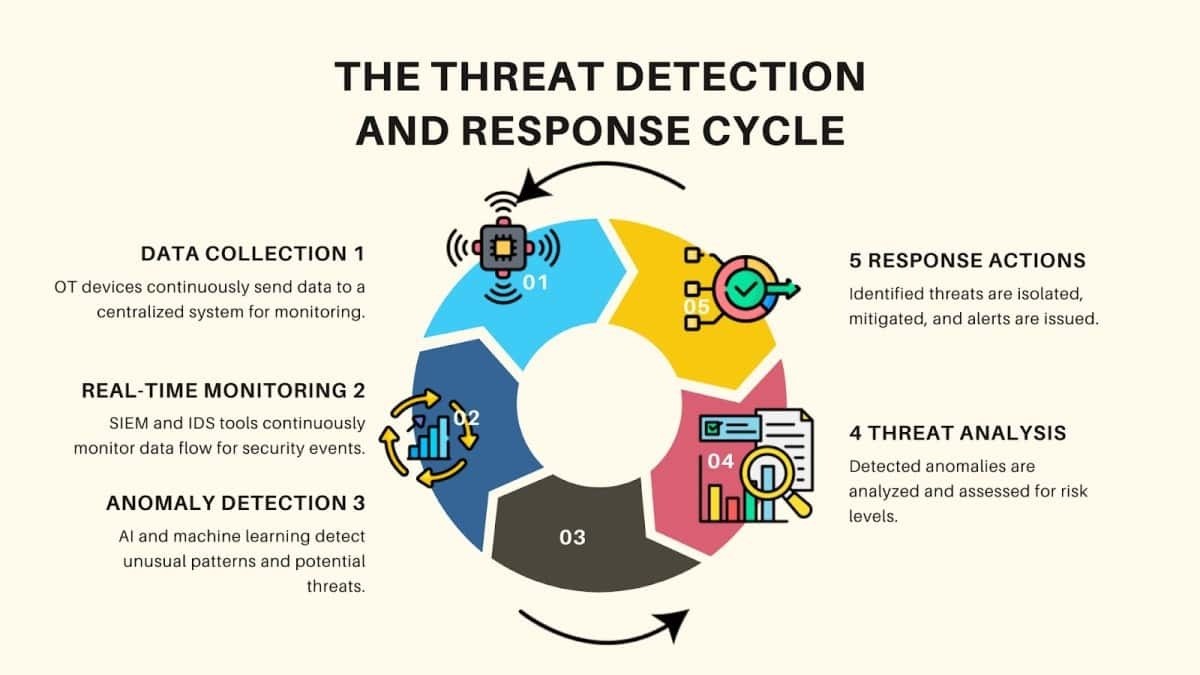
At the core of MDR is Endpoint Detection and Response (EDR). EDR constantly monitors all activity on laptops, servers, and mobile devices. It doesn't just look for known signatures; it monitors behavioural anomalies, such as unusual processes running or file access happening after hours.
2. The Human Element: 24/7 Threat Hunters
This is the major differentiator. The EDR tool feeds data to a remote team of experienced security analysts. These analysts:
- Proactive Threat Hunting: They actively look for subtle indicators of compromise (IOCs) that automated systems might miss.
- Rapid Containment: The moment a threat is verified, the MDR team can remotely isolate the affected device, preventing the attack from spreading laterally across the network.
- Expert Remediation: They provide clear, actionable steps to remove the threat, restore the system, and close the vulnerability gap, minimizing business downtime.
Why Business Leaders are Turning to MDR
For Business Leaders and IT Management, MDR is a strategic investment that delivers critical benefits:
- Immediate 24/7 Coverage: Eliminates the need to staff and train an internal security team, saving massive time and operational costs.
- Reduced Risk and Dwell Time: Significantly cuts the average time an attacker spends undetected in the network, turning potential major breaches into minor, contained incidents.
- Expertise on Demand: Provides access to specialized analysts who track the latest global threats, ensuring your defence is always current.
- Compliance Support: Generates detailed incident reports necessary for meeting compliance standards and proving due diligence.
Elevate Your Defence with NOCTeam MDR
Waiting for an incident to happen is no longer an option. NOCTeam’s Managed Detection and Response service brings the power of an enterprise-grade SOC to your business, affordably and effectively.
We deploy and manage EDR solutions, providing your organization with dedicated 24/7 monitoring and response expertise, so your IT team can focus on driving business value.
Are you confident your current antivirus can stop a sophisticated zero-day attack at 3 AM?
Contact NOCTeam today at [email protected] to learn how our MDR service can secure your future and for a free IT Assessment.
#MDR #CyberSecurity #EDR #SMBProtection #NOCTeam
Originally published on LinkedIn.